Gauteng Data Breach Raises Government Cybersecurity Questions
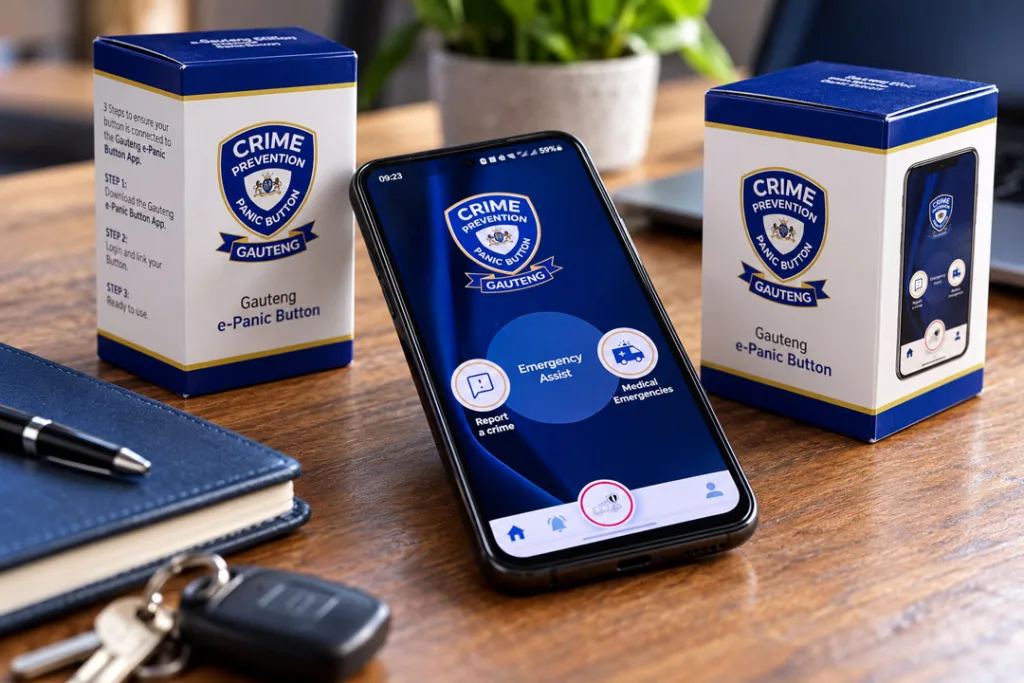
Johannesburg, South Africa — October 14, 2026 — A reported data breach involving Gauteng’s e-Panic Button application has raised serious questions about the protection of personal information, the government’s response to cybersecurity vulnerabilities, and the accountability of those responsible for systems entrusted with sensitive citizen data.
According to a report published by Newsday on October 13, the Gauteng Department of e-Government was alerted to a security vulnerability on September 21, 2026, by cybersecurity researcher and GroundUp journalist Joel Cedras. The application had approximately 280,000 registered users, although the full extent of the alleged exposure remains undetermined.
The department reportedly took approximately two weeks to notify the Information Regulator, which had not received the required security compromise notification by September 30.
Section 22 of the Protection of Personal Information Act (POPIA) requires organisations to notify the regulator and, where applicable, affected individuals, as soon as reasonably possible, when there are reasonable grounds to believe that personal information has been accessed or acquired by an unauthorised person.
The delay raises questions about the department’s incident-response procedures and whether its handling of the matter complied with its legal obligations.
Who Investigates a Government Data Breach?
Further concerns emerged over the decision to allow Evolve, the company responsible for developing and hosting the e-Panic Button application, to appoint its own investigator.
During a joint meeting of the Gauteng Provincial Legislature’s Portfolio Committee on e-Government and Community Safety, questions were raised about the independence of that investigation.
The preliminary investigation report is expected on October 20, 2026. Until its findings are made available, important questions remain unanswered, including when the vulnerability first emerged, how the exposure occurred, how many people were affected, and whether adequate security assessments were conducted before the system was deployed.
These are not minor technical details. The application is intended to help residents seek emergency assistance, including in circumstances involving domestic violence, assault and other threats to personal safety.
If a platform collects sensitive information to protect people, the security of that information becomes part of the protection it promises to provide.
The incident also raises questions about the appropriate distinction between identifying a security vulnerability and exploiting one. Newsday reports that the South African Police Service advised Evolve to open a criminal case against Cedras over allegations that his actions amounted to attempted hacking. The circumstances and merits of those allegations should be established through a properly conducted investigation.
Digital Government Requires More Than Assurances
The breach comes as South Africa accelerates its plans to digitise government services and introduce a national Digital ID system.
In an October 1 address, Home Affairs Minister Leon Schreiber confirmed that the department was progressing with the Digital ID project and processing public comments on the draft regulations. He stated that the system would be voluntary, that physical Smart ID cards would remain available and that the final regulations would impose limits on how personal data could be used.
The government’s stated objectives include improving access to services, reducing fraud and enabling citizens to use digital credentials to verify their identities.
Those objectives may offer practical benefits. However, the effectiveness of any such system depends on how its security, governance and accountability arrangements operate in practice.
The e-Panic Button incident does not establish that the proposed Digital ID system has the same vulnerabilities. It does, however, illustrate why the public should demand evidence of robust safeguards before entrusting increasingly sensitive personal information to digital government infrastructure.
Questions about cybersecurity cannot be answered by assurances alone. Independent penetration testing, clear incident-reporting procedures, meaningful oversight, and transparent investigations are essential components of public trust.
What Happens When Sensitive Data Is Exposed?
A compromised emergency-services platform presents risks that extend beyond the possibility of ordinary identity theft. Depending on what information was accessed, an exposure could potentially place people at risk by revealing personal circumstances, reports of abuse or other sensitive details.
The actual consequences of this incident remain subject to investigation. Nevertheless, it highlights a fundamental concern: citizens should not have to accept unnecessary risks simply because they rely on a government-supported service.
The same principle must inform the debate about Digital ID. A digital credential may make identification and access to services more convenient, but the broader digital infrastructure supporting it must be assessed for its security, resilience, and potential consequences of system failures.
The public also deserves clarity about which institutions and service providers can access identity information, how access is monitored, how long records are retained and what remedies are available when personal information is compromised.
The government’s Digital ID proposals and the e-Panic Button breach concern different systems. Their connection lies in the wider question of whether adequate protections, independent scrutiny and effective accountability will keep pace with the expansion of digital government.
Accountability Must Come Before Public Confidence
The immediate priority should be to establish the facts surrounding the e-Panic Button breach, determine the extent of the exposure and clarify whether the department and its service provider met their legal and contractual responsibilities.
The public should also be informed about the corrective measures taken, the findings of an independent investigation and any steps required to prevent a similar incident.
As South Africa expands its digital infrastructure, the standard of accountability should rise alongside the volume and sensitivity of the information being collected.
If a government department cannot yet establish the full extent of a reported data exposure, what evidence should citizens require before trusting larger digital identity systems with even more consequential personal information?
Related analysis: The Gauteng data breach raises broader questions about South Africa’s Digital ID ambitions, government accountability and the protection of personal information. Read our analysis on Casting Out Deceptions: South Africa’s Digital ID: Who Protects Our Data?
Source: Newsday — Government department waited two weeks to report data breach exposing 280,000 South Africans. Additional context: Gauteng Provincial Legislature statement and Home Affairs Minister’s October 1 address.